
Navigating GDPR Compliance: How Bransom’s bsmart2 Empowers Retailers with Robust Data Management
The implementation of the General Data Protection Regulation (GDPR) marked a pivotal moment for businesses globally, fundamentally reshaping how organizations manage and protect personal data. For any company that collects, processes, or stores data pertaining to its employees, customers, or suppliers, GDPR necessitated a thorough overhaul of existing data handling practices. This extensive legal framework, designed to standardize data protection laws across Europe and grant individuals greater control over their personal data, introduced significant new responsibilities and potential penalties for non-compliance.
The Dawn of GDPR: A New Era for Data Privacy
GDPR, which came into effect on May 25, 2018, established a comprehensive set of rules governing the processing of personal data. Its core principles revolve around transparency, lawfulness, fairness, data minimization, accuracy, storage limitation, integrity, confidentiality, and accountability. It emphasizes the rights of data subjects, including the right to access their data, the right to rectification, the right to erasure (also known as the “right to be forgotten”), and the right to object to processing. For businesses, this meant a heightened focus on understanding what data they hold, why they hold it, how long they keep it, and critically, how they secure it. The regulation’s extraterritorial scope means it applies to any organization anywhere in the world that processes the personal data of individuals residing in the European Union, making its impact truly global.
GDPR’s Direct Impact on the Retail Sector
Retailers, by their very nature, frequently interact with vast amounts of customer data. From transaction histories and purchase preferences to contact details for marketing communications and loyalty programs, customer data is central to modern retail operations. Post-GDPR, retailers faced unique challenges requiring a rigorous evaluation of their data ecosystems. Key areas of concern included:
- Customer Data Inventory: Identifying precisely what customer data is collected, where it is stored, and who has access to it.
- Consent Management: Establishing clear, unambiguous mechanisms for obtaining and recording customer consent for marketing communications across various channels (email, SMS, post, telephone). Consent must be freely given, specific, informed, and an unambiguous indication of the data subject’s wishes.
- Data Subject Rights: Developing robust processes to efficiently handle requests from individuals seeking copies of their personal data (Right of Access) or wishing to have their data deleted (Right to Erasure).
- Data Security: Ensuring appropriate technical and organizational measures are in place to protect personal data from unauthorized processing or accidental loss, destruction, or damage.
- Accountability: Demonstrating compliance with GDPR principles through comprehensive record-keeping and audit trails.
These requirements necessitated not just policy changes but often significant technological enhancements to existing systems to manage the lifecycle of customer data in a compliant manner.
Bransom bsmart2: Your Partner in GDPR Compliance
Recognizing the substantial burden these new regulations placed on its clients, Bransom, a leading provider of retail management systems, proactively enhanced the data management capabilities within its flagship bsmart2 platform. These enhancements are specifically designed to streamline compliance, making it easier and quicker for retailers to meet their GDPR obligations without disrupting their core business operations. Bransom’s bsmart2 now offers a comprehensive suite of tools that address the critical aspects of data access, deletion, consent management, and audit trailing, providing retailers with peace of mind and operational efficiency.
Comprehensive Data Access and Transparency
One of the fundamental rights granted by GDPR is the “Right of Access,” allowing individuals to request confirmation of whether their personal data is being processed, where, and for what purpose. They also have the right to obtain a copy of their personal data. Bransom’s bsmart2 has been equipped with sophisticated facilities that enable retailers to effortlessly fulfill these requests. Within the system, specifically through the enhanced Customer Marketing module, users can now quickly and accurately extract and print all of a customer’s details held on the system. This comprehensive report includes all relevant personal data, allowing retailers to provide customers with a clear and transparent overview of the information stored about them, thereby simplifying compliance with this crucial data subject right.
Ensuring the Right to Erasure: Secure Data Deletion
Another cornerstone of GDPR is the “Right to Erasure,” often referred to as the “right to be forgotten.” This right empowers individuals to request the deletion or removal of their personal data where there is no compelling reason for its continued processing. For retailers, managing such requests posed a significant challenge, requiring meticulous attention to ensure all relevant data across various systems could be identified and securely removed. Bransom’s bsmart2 directly addresses this by integrating robust data deletion capabilities. Should a customer request the removal of their personal data, retailers can now execute this action directly within bsmart2. Crucially, every deletion is accompanied by a comprehensive audit trail, documenting the action, the date, and the user who performed it. This audit trail is indispensable for demonstrating accountability and proving compliance to regulatory authorities, providing an irrefutable record of adherence to the right to erasure.
Streamlined Consent Management at Every Touchpoint
Obtaining and managing explicit consent for marketing communications is perhaps one of the most visible and impactful changes brought about by GDPR for retailers. Consent must be clear, specific, and easily withdrawn. Bransom’s bsmart2 introduces intelligent features designed to embed consent management seamlessly into the daily retail workflow, ensuring compliance without creating friction for staff or customers.
Point-of-Sale (POS) Integration for Proactive Consent
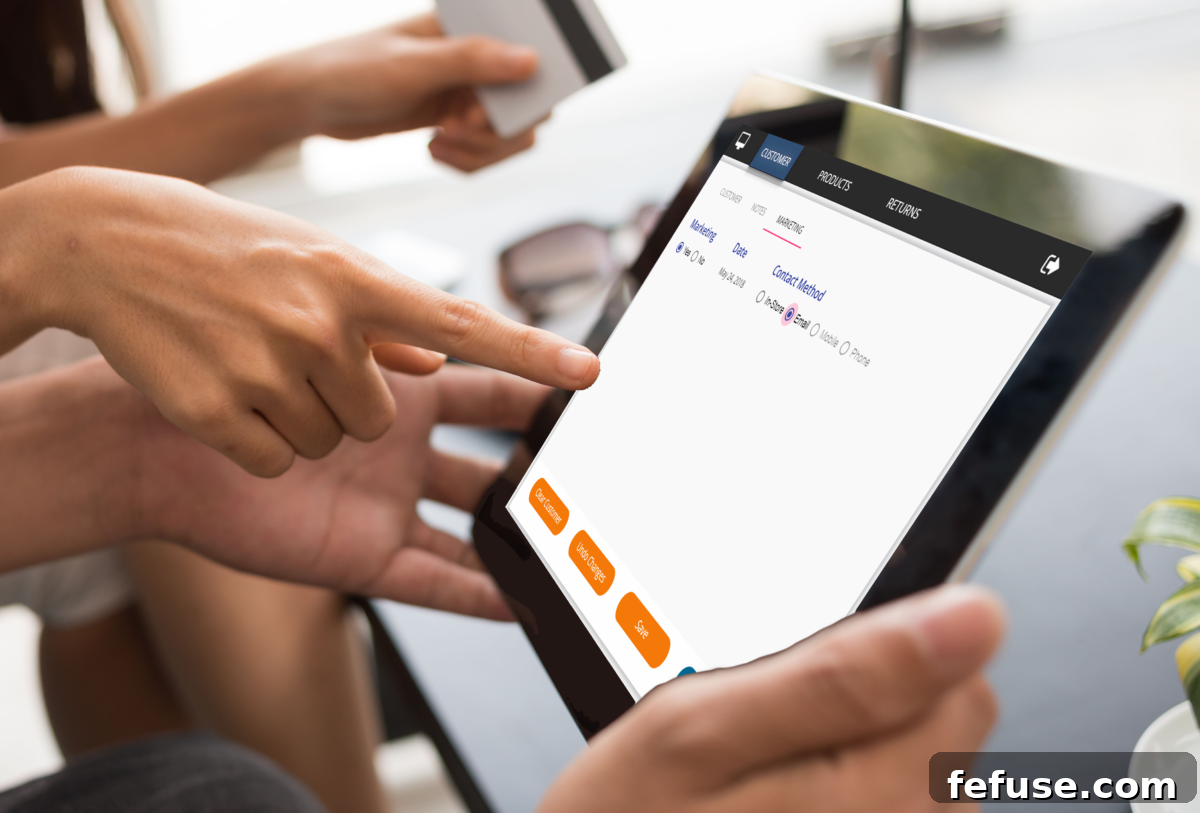
To ensure consent is gathered at the earliest possible opportunity, bsmart2 features a strategic pop-up window at the point-of-sale. This pop-up automatically appears when a new customer record is being created, serving as a timely reminder for counter staff to explicitly ask for the customer’s consent for marketing communications. The system allows for consent to be specified by method, including email, post, telephone, SMS, or other customizable channels, offering granular control over communication preferences. For existing customers, the system can be configured to prompt staff to update consent if a purchase is made after a pre-defined period of time, ensuring that consent records remain current and valid. Furthermore, custom text can be added to these prompts, guiding the operator through the consent process and providing essential information, such as references to the company’s privacy policy or instructions on how customers can unsubscribe in the future. This proactive approach at the POS significantly reduces the risk of non-compliant marketing activities.
Empowering Marketing with the Customer Marketing Module
Beyond the point-of-sale, the Customer Marketing module within bsmart2 has been significantly enhanced to further support GDPR compliance. This module now centralizes all customer marketing preferences and consent statuses, enabling retailers to segment their audience effectively based on explicit consent. It allows for detailed records of what type of marketing a customer has opted into (or out of) and through which channels. This functionality not only ensures that marketing efforts are compliant but also helps retailers to build trust by respecting customer choices, ultimately leading to more effective and targeted campaigns that resonate with willing recipients. The module also facilitates the management of data subject requests related to marketing preferences, making it straightforward to update consent or opt-out requests.
Unwavering Accountability with Robust Audit Trails
A core tenet of GDPR is accountability, requiring organizations to not only comply with the regulation but also to be able to demonstrate that compliance. Bransom’s bsmart2 system excels in this area by incorporating comprehensive audit trails for all critical data management actions. Whenever customer data is extracted, amended, or deleted, the system automatically logs the details of the action, including the date, time, and the user responsible. These robust audit trails are invaluable for internal governance, providing a clear record of all data-related activities. In the event of an audit or an inquiry from a data subject or regulatory authority, these trails serve as irrefutable evidence of the retailer’s commitment to GDPR principles, significantly mitigating compliance risks and demonstrating due diligence.
Beyond Compliance: Building Customer Trust and Operational Efficiency
While the initial driver for these enhancements was GDPR compliance, the benefits extend far beyond simply avoiding penalties. By implementing robust data management practices, retailers can foster deeper trust with their customer base. Transparency and respect for data privacy are increasingly important factors for consumers when choosing where to shop. A system like bsmart2, which visibly demonstrates a commitment to these values, helps build stronger customer relationships. Furthermore, by streamlining data access, deletion, and consent management, retailers can achieve significant operational efficiencies. Staff spend less time on manual, error-prone data handling tasks, allowing them to focus on core retail activities. The integrated nature of the solution ensures that data privacy is not an afterthought but an integral part of the daily operational fabric.
Industry Insight: Chris Garland on Bransom’s Commitment
Bransom managing director, Chris Garland, encapsulates the company’s dedication to its clients’ success in the face of evolving regulations: “The GDPR puts new responsibilities on both us and our clients, and we’ve developed these new features to make it easier and quicker for them to meet the GDPR obligations. Our proactive approach ensures that retailers can focus on serving their customers, confident that their data handling processes are fully compliant. The data access, deletion, and audit functions, in particular, are exceptionally comprehensive, providing an unparalleled level of control and transparency. We believe that empowering our clients with these tools is crucial for navigating the modern retail landscape successfully and sustainably.” This statement underscores Bransom’s understanding of the dual responsibility and their commitment to delivering practical, effective solutions.
Conclusion: Future-Proofing Retail with Smart Data Management
The GDPR fundamentally changed the landscape of data protection, making robust data management not just a legal necessity but a competitive advantage. For retailers, navigating these complex waters requires sophisticated tools that integrate seamlessly into their existing operations. Bransom’s bsmart2 system offers a powerful and comprehensive solution, empowering retailers to confidently manage customer data, obtain and track consent effectively, and fulfill data subject rights with ease and accountability. By investing in such a system, retailers are not merely complying with regulations; they are future-proofing their businesses, building invaluable customer trust, and ensuring long-term operational integrity in an increasingly data-conscious world.
News Source: professionaljeweller.com